TruffleHog Secrets Revocation Program
Live Resend API keys found in Docker images, Hugging Face datasets, and other public sources are now revoked automatically.
In July, we became a GitHub secret scanning partner. Any Resend key exposed on public GitHub is revoked automatically.
GitHub's program covers public GitHub repositories and npm, and yet many keys leak in other locations like Docker images, packages, other registries, and public datasets.
Today, we're announcing that Resend is a launch partner in TruffleHog's Secrets Revocation Program. TruffleHog scans public code, packages, container images, and datasets for exposed keys. When it finds a working Resend key, it reports it to us and we revoke it automatically.
Where TruffleHog looks
TruffleHog adds another route for finding exposed keys across:
- Docker Hub images
- Hugging Face datasets
- PyPI and npm packages
- GitLab repositories
- Android apps and Firefox add-ons
- New pushes to GitHub
What happens when a key leaks
- Verified as live: TruffleHog tests every key it finds and reports keys that still work.
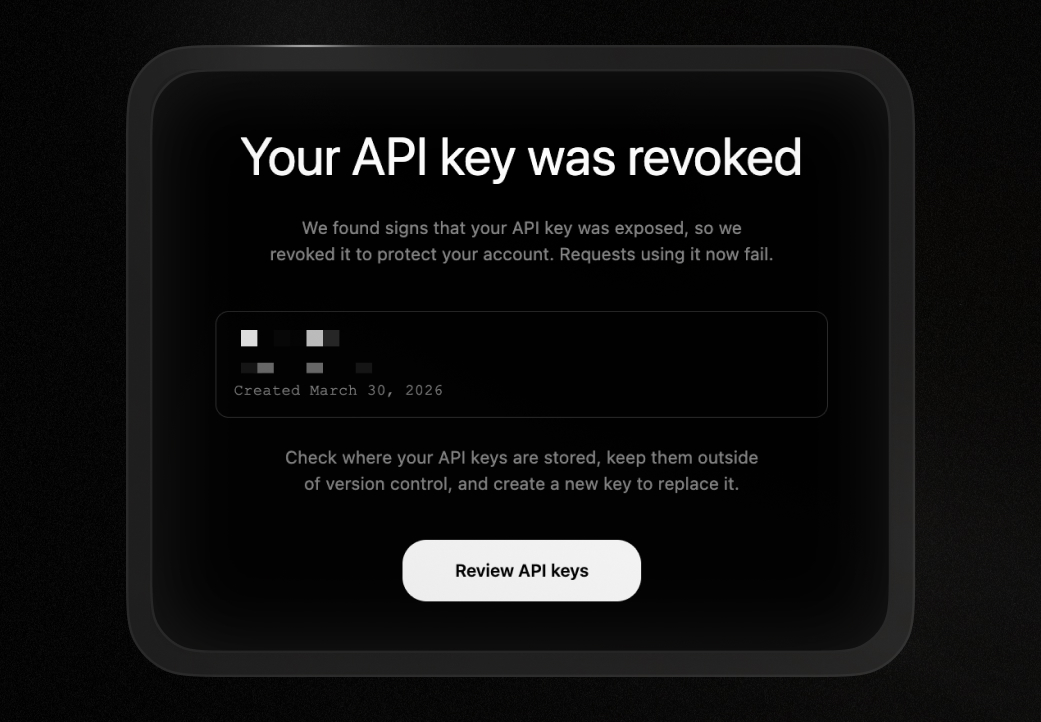
- Revoked automatically: We disable the exposed key as soon as the report arrives.
- Your team is notified: We email all admins with a link to where the key was found.
This security protection is on by default for every Resend account.
Why we revoke instead of warn
TruffleHog found that 81% of the leaked keys it reported last year were still live six months later. A warning email leaves the key working until someone acts on it.
For email, a live leaked key means anyone can send spam or phishing from your verified domain, endangering your recipients and your sending reputation. If the leak endangers your sending reputation, it can take weeks to rebuild.
To protect you and your recipients, revoking the key immediately closes that window.
Conclusion
Between GitHub and TruffleHog, a leaked Resend key gets caught in far more places than before, and it's revoked before it can hurt your sending reputation. View the TruffleHog announcement post for more details on the program.
If you have any questions, please reach out to us and we'll be happy to help.